Coffee Loyalty App Privacy In Malaysia And Jakarta: What Consumers And Businesses Need To Know For 2026
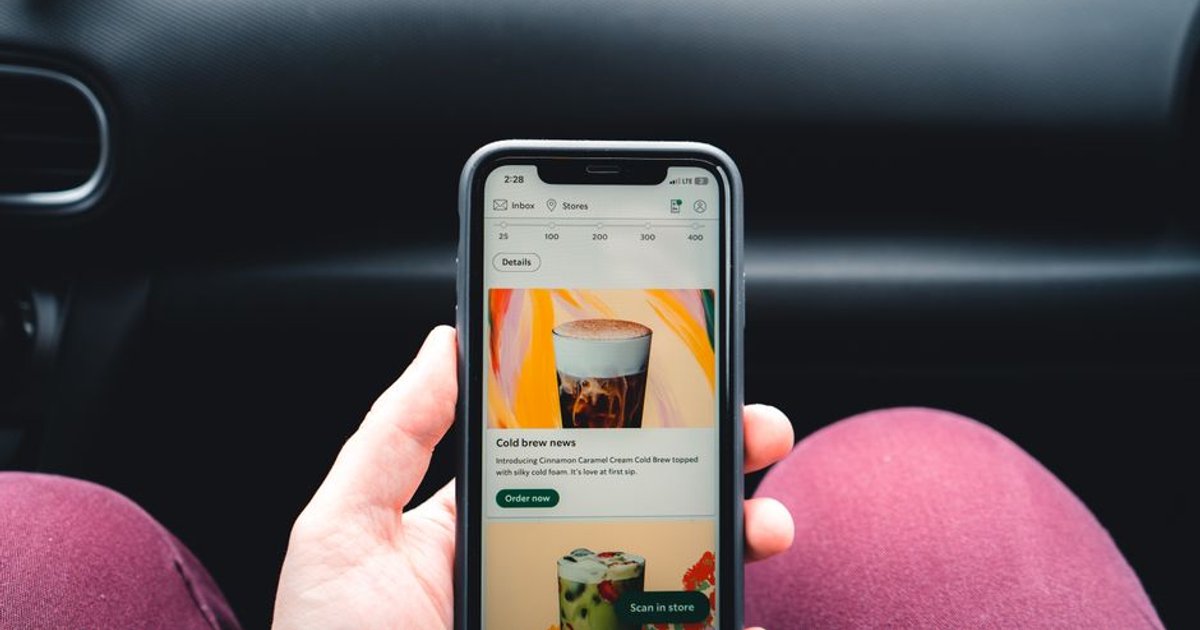
Coffee Loyalty Apps in Malaysia and Jakarta: Unmasking Data Privacy and the Next Wave of Consumer Trust
Coffee, often described as the backbone of urban culture, is more than just a beverage in Malaysia and Jakarta; it is a ritual, a community, and a booming business. As the café landscape has evolved over the past decade, digital loyalty apps have become indispensable tools for both brands and customers. These platforms, once mere stamp cards now transformed by technology, promise personalized rewards, seamless payments, and hyper-relevant offers. However, behind their friendly interfaces lies an intricate web of information collection and sharing practices that increasingly shape consumer experiences, business models, and regulatory scrutiny. This exposé dives deep into the real-world data flows, strategies, and risks underpinning coffee loyalty in Southeast Asia, charting a path for households and businesses as privacy moves to center stage.
The Rise of Coffee Loyalty Apps: Tradition Meets Digital Innovation
Historical Context and Market Boom: The Malaysian and Jakarta café scenes have seen an explosion in digital loyalty app adoption. In Malaysia alone, the urban café market is valued at over RM 50.8 billion, with major brands like Starbucks, Zus Coffee, and local groups investing heavily in app-based engagement.
Technological Leap: The transition from physical loyalty cards to digital apps has been swift. Apps now combine advanced identity recognition, targeted marketing, and AI-powered recommendation engines. These innovations are driven by first-party data strategies, as brands seek direct relationships with customers, bypassing marketplace dependency and integrating payment, location, and behavioral feedback into their commercial fabric.
Consumer Experience: For shoppers and coffee lovers, the promise is clear: faster ordering, exclusive rewards, and relevant perks. Yet, the convenience comes with a price, data about where you go, what you buy, and even who you are is stored, analyzed, and often shared.
Beyond Points: What Loyalty Apps Really Collect
Unpacking the Data Spectrum: Modern coffee apps gather a wide array of information. At minimum, they capture your name, email, phone number, date of birth, gender, and nationality. Financial information, including card details and purchase history, is bundled with location tracking that can pinpoint your movements to specific neighborhoods, outlets, or even workplace corridors. Behavioral data, product views, searches, clicks, and preference information (favorite drinks, dietary options) are analyzed to shape marketing campaigns.
App-Store Disclosures: Recent Google Play listings for Kopi Kenangan and Starbucks Malaysia reveal possible sharing of location, personal, and financial data with third parties, while Point Coffee in Indonesia claims no external sharing but admits broad internal collection.
The Commercial Value: Brands use this data to forecast demand, personalize offers, and identify high-value customers. They can distinguish between early morning buyers, delivery enthusiasts, and discount hunters, optimizing supply chains and campaign timing.
Privacy Risks: The same information can reveal sensitive patterns: religious routines inferred from purchase timing, health status, or residential and workplace habits. Location, in particular, is often more revealing than any single transaction.
Malaysia’s Regulatory Landscape: Navigating the PDPA and AI Frontiers
Personal Data Protection Act 2010 (PDPA): Malaysia’s primary privacy law, overseen by the Personal Data Protection Department (JPDP), sets standards for transparency, consent, purpose limitation, and data security. Loyalty app providers must explain their reasons for collection, obtain informed consent, secure personal data, and offer avenues for access, correction, and withdrawal.
Emerging AI and Data Protection Framework: In 2026, Malaysia launched a draft Artificial Intelligence and Personal Data Protection Framework, signaling a new chapter for brands using AI to segment customers, detect fraud, and drive dynamic promotions. The consultation process, with a submission deadline of 23 October 2026, presses businesses to rethink the inputs and governance of AI systems fed by loyalty app data.
Consumer Rights: Consumers can request access to their data, correct inaccuracies, and withdraw consent, including for direct marketing. However, app-store summaries are often vague, omitting specifics about retention, third-party sharing, profiling, and cross-border transfers. Thus, reading the full privacy notice is essential.
Jakarta and Indonesia: A New Era of Data Governance
Personal Data Protection Law and Regulation No. 33 of 2026: Jakarta’s privacy regime, newly refined, is shaped by Indonesia’s sweeping personal data protection legislation. The implementation of Government Regulation No. 33 of 2026 marks an inflection point, with compliance required by 16 January 2027.
Complex Data Ecosystem: Loyalty apps in Jakarta often involve multiple parties: the brand, app developer, payment gateway, delivery platform, CRM vendors, and group companies, sometimes located outside Indonesia. The distinction between data controllers and processors becomes critical, as sharing with subsidiaries, affiliates, or external partners raises questions of accountability and risk.
Practical Implications: Location and behavioral data is especially prized in Jakarta’s dense urban context where commuting routes, office districts, and shopping patterns can be inferred. Starbucks Indonesia’s privacy policy, for example, details retention practices, eligibility restrictions for users under 18, and cross-border considerations.
Children’s Privacy: Loyalty apps are not intended for minors, yet shared family devices and parent payment methods complicate enforcement and risk.
The Reality of App Disclosures: What the Labels Don’t Tell
Encrypted in Transit, Not Everywhere: Apps typically advertise encryption during transmission, which protects information from interception. But this does not guarantee secure storage or processing within the company or its partners.
Collection vs. Sharing: Declaring “no data shared” does not equate to minimal internal collection. Brands may use data for internal profiling, marketing, and AI without external transfer.
Opaque Data Practices: App-store summaries lack detail on retention periods, profiling, deletion methods, and cross-border transfers. Only full privacy notices reveal the operational realities, and even these are often written in legalese, not consumer-friendly language.
Risks and Red Flags: What Consumers Must Watch For
Over-Collection: Many apps collect more than necessary, such as continuous location tracking, date of birth, gender, and device information unrelated to loyalty services. This amplifies breach impact and complicates privacy notices.
Excessive Marketing: Registration frequently bundles consent for promotional marketing, with notifications and ads delivered across push, SMS, email, and in-app channels. Consumers may lose essential service access if they opt out.
Location Tracking: Apps justify location for store discovery and order fulfillment, but persistent background tracking is more intrusive. “While using the app” access, manual outlet selection, and approximate location are preferable.
Payment Exposure: Financial data, including card numbers and tokens, are at risk in the event of a breach. Consumers should ensure apps use trusted payment processors and avoid retaining sensitive card information.
Profiling and Price Discrimination: Loyalty data powers segmentation and personalisation, but opaque profiling can produce unfair differences in offers, aggressive re-engagement, and automated decisions that lack transparency.
Cross-Border Transfers: Many brands use global cloud servers and analytics partners. Consent clauses often include transfers outside national borders, making clarity about categories, purposes, and safeguards essential.
Account Takeover: Weak authentication leads to fraud, reward theft, and unauthorized purchases. Brands should implement multifactor authentication, login alerts, and account recovery procedures.
Comparative Insight: Malaysia Versus Jakarta, Same Risks, Different Strategies
Regulatory Maturity: Malaysia’s PDPA is longstanding but is now challenged by AI-driven profiling and international data flows. The country’s draft AI framework is a proactive step but lacks immediate enforceability.
Jakarta’s Transition: Indonesia’s regulation is newly effective, giving brands a six-month window to prepare for robust requirements. Jakarta’s urban density and complex vendor ecosystem raise the stakes for data minimization and security.
Consumer Rights: Both jurisdictions empower consumers to access, correct, and delete their data, but practical implementation varies. Account deletion rarely erases legal or settlement records, and consent withdrawal for marketing is often bundled awkwardly.
Children’s Safeguards: Both regions caution against loyalty apps for minors, yet enforcement is challenging, especially with shared devices.
Location Sensitivity: In Malaysia, approximate location suffices for many purchases. In Jakarta, precise urban mapping makes location data more valuable, and risky, especially as brands experiment with predictive analytics and demand forecasting.
Innovative Privacy Practices: Tactical Shifts for Brands and Households
Data Minimization: Leading brands now build data inventories, mapping each category, point of collection, purpose, storage location, retention period, internal and external users, and deletion methods.
Granular Consent: New-generation apps increasingly offer separate controls for account creation, service messages, promotional marketing, personalized offers, location services, and third-party advertising.
Readable Notices: Privacy notices are being rewritten to answer five consumer questions: What is collected? Why? Who receives it? How long is it kept? How can rights be exercised? Notices are now translated into Bahasa Malaysia and Bahasa Indonesia where relevant.
Vendor Governance: Contracts with payment, cloud, analytics, and marketing partners are being updated to specify permitted purposes, security standards, breach notification, data deletion, audit rights, and restrictions on independent reuse.
Loyalty Value Protection: Brands implement fraud alerts, redemption limits, risk-based authentication, device monitoring, and transparent recovery for lost rewards.
AI Governance: As AI becomes central, brands document models, inputs, profiling practices, correction procedures, retention schedules, vendor data reuse, and human review availability. Anonymization is no longer assumed effective; location, timestamp, and pattern data can re-identify individuals.
Household Action Plan: Empowering Consumers
Pre-Installation: Only download from official sources, check developer credentials and update history, review data-safety summaries, read privacy notices, avoid unofficial APKs, and scrutinize permissions for location, contacts, mic, camera, or Bluetooth.
Registration: Provide only necessary info, use unique passwords, decline optional marketing, avoid saving payment details on shared devices, and use a dedicated email for retail promotions.
Post-Installation: Set location to “while using,” review permissions monthly, disable unnecessary background activity, turn off excessive marketing notifications, remove old payment methods, monitor account activity, and keep apps updated.
Account Closure: Request deletion of the account, optional marketing profiles, and promotional lists. Confirm what is retained for legal or accounting purposes, access stored information before deletion, and correct inaccuracies.
Children’s Use: Supervise app installation, limit permissions, educate on privacy basics, and avoid registration for minors.
Industry Action Plan: Building Trust and Operational Excellence
First 30 Days: Map all data collected, audit app permissions, separate mandatory messages from marketing, confirm deletion and access workflows, and test removal from promotional lists.
Days 31, 60: Rewrite privacy notices for clarity, implement granular consent controls, restrict location collection, review payment data handling, strengthen authentication, update vendor contracts, and train customer service staff.
Days 61, 90: Assess privacy and security for AI features, test deletion and correction processes, launch privacy dashboards, establish retention schedules, report metrics to management, and prepare for Indonesia’s January 2027 regulation.
Metrics to Track: Registration completion, permission acceptance, opt-in rates, active loyalty users, repeat purchase rate, uninstall rate, privacy complaints, deletion requests, fraudulent redemption rate, and time to resolve rights requests.
Forward-Looking Commercial Implications
Trust as Growth Lever: Transparency in privacy boosts registration and deepens engagement. Explaining value, like “We use order history for relevant rewards” or “Location helps find nearby outlets”, is more effective than generic legal notices.
First-Party Data: Direct relationships support repeat purchases, feedback loops, local promotions, product testing, and churn prevention, but only if customers trust the brand’s handling of their data.
Privacy and Cost: Intrusive apps generate negative reviews and more uninstallations. Transparent privacy practices reduce acquisition costs, support conversion, and lower customer-support load.
Experimental Approach: Brands should validate claims on personalisation impact via privacy-safe A/B tests, comparing rewards, consent explanations, location types, and notification strategies. Incremental revenue, not mere clicks, is the goal.
Household Service Partners: Companies like GoodHelp can offer practical privacy checklists, app-permission reviews, account deletion support, scam education, household audits, and children’s app guidance, positioning themselves as trusted partners rather than generic information sources.
Key Distinctions for All Stakeholders
- Encryption: “Encrypted in transit” protects against interception, but does not guarantee data safety at rest or during processing.
- Sharing vs. Collection: No third-party sharing does not mean minimal internal collection or profiling.
- Consent: Consent should not justify collection of information irrelevant to the service.
- Deletion: Account deletion may not remove records required by law.
- Personalisation: Profiling can be beneficial if clearly disclosed and opt-out is practical.
- Privacy Policy: Written policy does not assure operational effectiveness.
- App-Store Label: Labels are summaries, not complete audits.
- Regulatory Preparation: Action should precede formal implementation dates.
Privacy is not a compliance checkbox but a strategic asset; brands that treat transparency as a core product feature will turn trust into sustainable growth, while consumers who take control of permissions and data choices will lead the shift toward a safer, more rewarding digital café culture.
Conclusion: The Road Ahead, Privacy as the Currency of Trust and Growth
Coffee loyalty apps in Malaysia and Jakarta are no longer just gateways to rewards; they are engines of data collection, personalisation, and commercial innovation. The trajectory of this industry hinges on how brands and households reconcile convenience with privacy. As regulations become stricter and consumer awareness grows, tactical shifts, data minimization, granular consent, transparent notices, robust vendor governance, and AI accountability, are not just good practice but competitive necessity.
For businesses, proactive privacy stewardship will unlock growth, deepen engagement, and reduce risk. For households, selective participation, strong passwords, controlled permissions, and assertive request management are the keys to digital safety. The ecosystem’s value will depend less on the volume of data collected and more on the quality of consent and trust built. In this new era, privacy is not a barrier to innovation but its foundation.
Strategically, the coffee industry must reimagine loyalty not only as a tool for retention but as a signature of brand integrity. The brands that lead with privacy will own tomorrow’s customer relationships, and the households that demand clarity will shape the evolution of Southeast Asia’s café culture. The time for action is now, before the next regulatory deadline or the next breach. Trust, once earned, will be the most valuable reward of all.